The best container security tools in 2027 help teams identify vulnerabilities, scan container images, monitor running workloads, and detect suspicious activities. Some tools focus on a specific security task, while others provide broader protection for containers, Kubernetes clusters, and cloud environments.
Container technology helps developers build, package, and deploy applications quickly. However, containers can introduce security risks when they contain vulnerable software, exposed secrets, outdated packages, or unsafe configurations. Businesses need reliable security practices to protect their applications throughout development and deployment.
What Are Container Security Tools?
best container security tools in 2027 are software solutions that help protect containerized applications from vulnerabilities, configuration mistakes, unauthorized access, and runtime threats. They can inspect container images before deployment, evaluate infrastructure configurations, and monitor applications while they are running.
Containers package applications and their dependencies into portable units. Although this approach improves consistency and deployment speed, a vulnerable library or incorrectly configured container can create risks across an application environment.
Security tools address these risks at different stages of the software development lifecycle. For example, a developer might scan an image before publishing it to a registry, while a security team monitors production containers for suspicious behavior.
An effective container security strategy usually combines vulnerability scanning, configuration checks, access controls, and runtime monitoring instead of relying on a single tool.
Why Are Container Security Tools Important in 2026?
Container environments can change frequently as teams deploy new application versions, update dependencies, and scale workloads. Without appropriate security controls, these changes can introduce weaknesses that are difficult to identify manually.
Container security tools help organizations:
- Identify vulnerabilities: Detect known weaknesses in operating system packages and application dependencies.
- Improve image security: Find risky components before an image reaches production.
- Detect suspicious activity: Monitor running containers for unusual processes or unexpected system behavior.
- Reduce configuration risks: Identify insecure Kubernetes settings and excessive permissions.
- Support compliance: Generate security reports and help teams document their controls.
- Prioritize remediation: Focus on vulnerabilities that pose the greatest risk to important applications.
These capabilities are particularly useful for organizations that deploy applications through automated CI/CD pipelines or manage multiple Kubernetes clusters.
Key Features to Look for in Container Security Tools
Before selecting a solution, identify the security problems you need to solve. The best tool for a small development team might not provide everything required by a large enterprise.
- Vulnerability and Image Scanning: Look for tools that inspect container images for known vulnerabilities in operating system packages and application dependencies. Some scanners also identify exposed secrets, risky configuration settings, and software component information.
- Runtime Threat Detection: Image scanning identifies potential problems before deployment, but it cannot detect every threat that appears while an application runs. Runtime security tools monitor activity and alert teams to suspicious behavior, such as unexpected shell execution or unauthorized file changes.
- Kubernetes Security: If your applications run on Kubernetes, evaluate whether the tool supports cluster configuration checks, workload monitoring, security policies, and Kubernetes-specific threat detection.
- CI/CD Integration: Security checks are more useful when developers can run them during development and deployment. Consider integrations with source repositories, build pipelines, container registries, and deployment workflows.
- Cost and Ease of Use: Compare licensing models, deployment requirements, reporting features, and ongoing maintenance. An open-source tool may reduce licensing expenses, but your team will still need time and expertise to configure and maintain it.
12 Best Container Security Tools in 2027
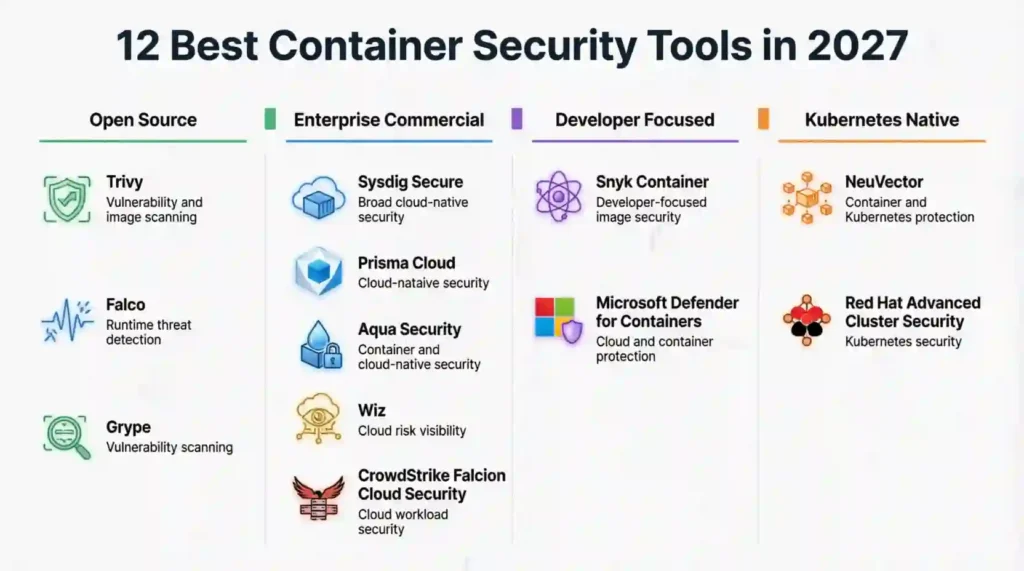
The following container security tools cover different needs, from open-source image scanning to enterprise cloud security platforms. Their capabilities overlap, but they are not direct substitutes for one another.
1. Trivy
Trivy is an open-source security scanner widely used to examine container images, filesystems, repositories, and other supported targets. It can identify known vulnerabilities and, with the relevant scanners enabled, detect secrets and misconfigurations.
Key features:
- Container image vulnerability scanning
- Detection of exposed secrets
- Supported misconfiguration checks
- Integration into development workflows
Best for: Developers, small teams, and organizations looking for a flexible open-source scanner.
Trivy is a useful starting point when a team needs to check images before deployment without immediately adopting a commercial security platform. Its coverage depends on the target, scanner settings, and available vulnerability data. Official Trivy documentation.
2. Falco
Falco is an open-source cloud-native runtime security project. It observes system and workload activity, evaluates events against security rules, and generates alerts when behavior matches suspicious patterns.
Key features:
- Runtime threat detection
- Customizable detection rules
- Monitoring of system activity
- Integration with Kubernetes and alerting workflows
Best for: Teams that need visibility into suspicious activity in running containers and Kubernetes environments.
Falco complements image scanners rather than replacing them. Its core purpose is detection and alerting; additional controls or integrations may be required to block or automatically respond to threats. Official Falco documentation.
3. Sysdig Secure
Sysdig Secure is a commercial cloud-native security platform that combines vulnerability management, runtime threat detection, and cloud and Kubernetes security capabilities.
Key features:
- Container vulnerability management
- Runtime threat detection
- Kubernetes security posture monitoring
- Investigation and reporting capabilities
Best for: Organizations that need broader visibility into containerized workloads and cloud environments.
Sysdig Secure can help security teams connect vulnerability findings with information about running workloads. This context can help prioritize issues that present a more immediate risk. Official Sysdig documentation.
4. Snyk Container
Snyk Container focuses on identifying vulnerabilities in container images and helping developers address problems in their software dependencies.
Key features:
- Container image vulnerability testing
- Continuous image monitoring
- Software bill of materials (SBOM) generation through supported commands
- Developer-oriented security workflows
Best for: Development teams that want to integrate container scanning into their existing software development process.
Snyk can help developers discover vulnerable dependencies earlier and evaluate remediation options. Teams should review the current product plan and supported integrations before choosing it. Official Snyk documentation.
5. Aqua Security
Aqua Security provides container and cloud-native application security capabilities designed to protect applications across development and deployment.
Key features:
- Image vulnerability scanning
- Container and Kubernetes security capabilities
- Policy-based security controls
- Support for cloud-native application protection workflows
Best for: Organizations seeking a broader security solution for containerized applications.
Aqua Security may suit teams that want to combine development-time checks with controls for deployed workloads. Evaluate the specific features included in the selected offering.
6. Wiz
Wiz is a cloud security platform that helps organizations identify and prioritize risks across cloud environments. Its capabilities can help teams understand how container-related vulnerabilities connect with cloud exposure and other security issues.
Key features:
- Cloud risk visibility
- Contextual risk prioritization
- Identification of relationships between security issues
- Cloud security posture analysis
Best for: Organizations managing complex cloud environments that need a broader view of connected risks.
Wiz is not simply a standalone image scanner. Teams should evaluate its container-related capabilities alongside their existing image scanning and runtime controls.
7. Prisma Cloud
Prisma Cloud, from Palo Alto Networks, offers cloud-native security capabilities for organizations that need to manage risks across applications and infrastructure.
Key features:
- Cloud security posture management
- Container and Kubernetes security capabilities
- Vulnerability and configuration risk visibility
- Policy and compliance support
Best for: Enterprises that need security controls across multiple cloud workloads and development stages.
Before purchasing, confirm which capabilities are available in the current edition and how they integrate with your cloud infrastructure.
8. Crowd Strike Falcon Cloud Security
Crowd Strike Falcon Cloud Security provides cloud security capabilities that can help organizations identify and investigate risks across cloud workloads.
Key features:
- Cloud workload risk visibility
- Security monitoring and investigation
- Risk prioritization
- Integration with the broader Falcon security ecosystem
Best for: Teams already using Crowd Strike or organizations seeking connected cloud security operations.
Its suitability depends on your cloud architecture, licensing, and the specific container security functions you require.
9. Neu Vector
Neu Vector is a container security tools in 2027 and Kubernetes security solution associated with SUSE. It focuses on protecting cloud-native workloads through security controls and monitoring.
Key features:
- Container and Kubernetes security
- Network and workload protection capabilities
- Security policy enforcement
- Integration with cloud-native environments
Best for: Organizations seeking Kubernetes-focused security controls.
Check the current SUSE product documentation for supported deployment options, licensing, and feature availability before implementing Neu Vector.
10. Microsoft Defender for Containers
Microsoft Defender for Containers is part of Microsoft’s cloud security offerings and helps protect supported containerized environments.
Key features:
- Container-related security findings
- Kubernetes security posture capabilities
- Vulnerability assessment integrations
- Security recommendations for supported environments
Best for: Organizations using Microsoft Azure and supported Kubernetes environments.
The available capabilities depend on the environment and subscription. Review Microsoft’s current documentation to confirm requirements and coverage.
11. Red Hat Advanced Cluster Security
Red Hat Advanced Cluster Security for Kubernetes helps organizations secure Kubernetes workloads and clusters through security management and policy controls.
Key features:
- Kubernetes security posture management
- Vulnerability management capabilities
- Network policy visualization and enforcement features
- Compliance and risk assessment support
Best for: Teams running Kubernetes at scale, particularly those using Red Hat Open Shift.
Its value depends on your Kubernetes architecture and the security controls already available in your environment.
12. Grype
Grype is an open-source vulnerability scanner for container images and filesystems. It helps identify known vulnerabilities in software components.
Key features:
- Container image vulnerability scanning
- Filesystem scanning
- Vulnerability reporting
- Integration with software security workflows
Best for: Developers and security teams seeking an open-source option for vulnerability detection.
Grype is focused on vulnerability scanning, so teams may need separate tools for runtime monitoring, secrets detection, and Kubernetes policy enforcement. Review the official Grype project for supported targets and usage details.
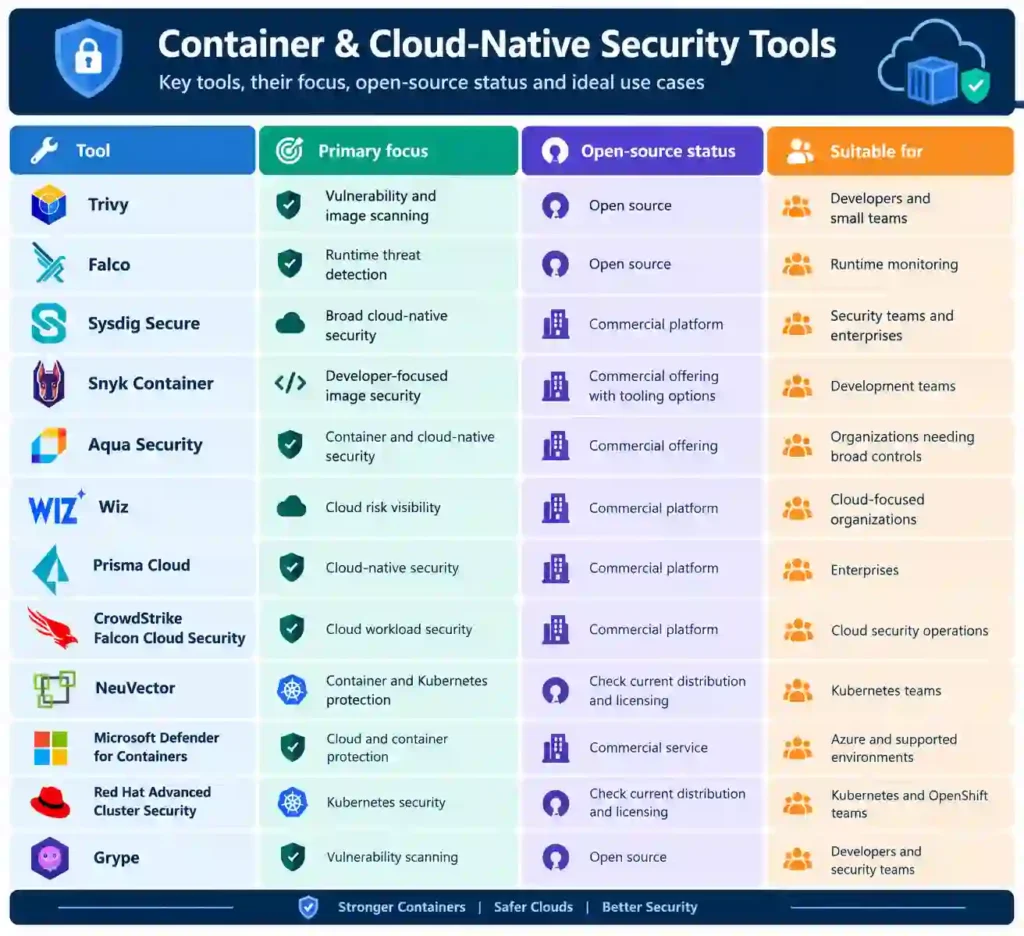
Container Security Tools Comparison: Features and Use Cases
The following table provides a high-level comparison. It is not a substitute for checking current product documentation or testing tools in your own environment.
Best Container Security Scanning Tools for Vulnerability Detection
container security tools in 2027 scanning tools inspect images and software components to identify known vulnerabilities before they reach production. They can be integrated into development workflows so teams can discover issues earlier.
Trivy and Grype are useful open-source options for vulnerability scanning. Snyk Container adds developer-focused testing and monitoring workflows, while Sysdig Secure and other commercial platforms can combine scanning with broader security capabilities.
When comparing scanning tools, check the vulnerability databases they use, the image formats they support, their reporting quality, and whether they can run automatically in your CI/CD pipeline.
A scan is only one part of security. Teams must review findings, prioritize serious issues, apply fixes, and rescan affected images. A clean scan does not guarantee that an application is completely secure.
How to Choose the Right Container Image Security Tool
A container image security tool examines an image for problems before it is deployed. Depending on its capabilities, it may identify vulnerable operating system packages, application dependencies, exposed secrets, or insecure configuration.
Trivy is a practical open-source starting point for several types of image checks. Grype is another option when vulnerability detection is the primary requirement. Snyk Container may suit teams that want developer-focused workflows, while broader platforms can connect image findings with runtime and cloud risks.
To select the right container image security tool, consider:
- Coverage: Does it scan the image formats and package ecosystems you use?
- Accuracy: Can your team understand and validate its findings?
- Automation: Can scans run automatically when images are built or updated?
- Remediation: Does it help developers identify fixes?
- Reporting: Can it produce reports suitable for your team and compliance requirements?
The right choice depends on your workflow, infrastructure, and risk tolerance rather than the number of features advertised.
Open-Source Container Security Tools: Are They Enough?
Open-source container security tools in 2027 tools can provide valuable protection without requiring a commercial platform license. Trivy and Grype support vulnerability scanning, while Falco focuses on runtime detection.
These tools can be effective when teams have the technical expertise to configure them, update their data sources, interpret findings, and maintain their integrations. However, open-source does not automatically mean zero cost: implementation, infrastructure, training, and maintenance all require resources.
Commercial platforms may offer centralized dashboards, vendor support, additional integrations, and broader security capabilities. Some organizations use a combination of open-source scanners and commercial monitoring products.
The best approach is to identify your security requirements first, then compare open-source and commercial options against those requirements.
How to Choose the Best Container Security Tools for Your Needs
Choosing a tool starts with understanding your environment. A small development team may need an image scanner that fits into an existing pipeline, while an enterprise may need centralized monitoring across many Kubernetes clusters.
Use these steps to guide your decision:
- Identify your main risk: Decide whether you primarily need vulnerability scanning, runtime detection, Kubernetes security, or broad cloud visibility.
- Map your workflow: Check where images are built, stored, tested, and deployed.
- Test representative workloads: Run shortlisted tools against real images and configurations.
- Review integration requirements: Confirm compatibility with your registries, orchestration platforms, and CI/CD systems.
- Compare total cost: Include licensing, deployment, training, maintenance, and support.
- Create a remediation process: Assign responsibility for investigating and fixing findings.
- Review coverage regularly: Reassess controls as applications, dependencies, and infrastructure change.
A layered strategy is often more effective than expecting one product to solve every container security problem.
Frequently Asked Questions
1. What is a security container?
A container security tools in 2027 can refer to a container used for secure storage or transport, such as a locked container for valuable or sensitive items. In software and cybersecurity, however, a container is an isolated environment that packages an application and its dependencies. Container security tools protect these software environments from vulnerabilities, unsafe configurations, and threats.
The meaning depends on whether the discussion concerns physical security or software technology.
2. What is a Class 5 security container?
The term “Class 5 security container” can refer to a classification used in particular physical-security or secure-storage standards. Its exact meaning depends on the standard, jurisdiction, and type of container. It is not a standard category of software container security tools.
For software security, it is more useful to identify the container platform, image format, and threat model you need to protect rather than apply a physical-container classification.
3. What are the 5 C’s in security?
There is no single universally accepted set of “5 C’s” used across all cybersecurity frameworks. Different organizations and training materials use different versions of the phrase.
For container security, focus on practical controls such as configuration management, access control, continuous monitoring, vulnerability checking, and compliance. These areas help teams reduce risk across development and production environments.
4. What are the top 5 security testing tools?
The best tools depend on the type of testing required. For container and cloud-native environments, five useful options to evaluate are:
- Trivy: Open-source vulnerability and container image scanning.
- Grype: Open-source vulnerability scanning.
- Falco: Runtime threat detection.
- Snyk Container: Developer-focused container vulnerability testing.
- Sysdig Secure: Broader container, Kubernetes, and cloud-native security capabilities.
These tools serve different purposes, so they should not be treated as identical alternatives. Select them according to your required coverage and workflow.
5. What is the best free container security tool?
Trivy is a strong starting point for teams that need an open-source container scanner. It can detect known vulnerabilities and supports additional scanning functions for supported targets. Grype is another good option when vulnerability detection is the main requirement. Falco is useful for runtime threat detection.
The best choice depends on whether you need image scanning, runtime monitoring, or both.
Conclusion
The container security tools in 2027 help teams discover vulnerabilities, detect suspicious behavior, and improve the security of containerized applications. Trivy and Grype are useful open-source options for vulnerability scanning, while Falco focuses on runtime detection. Commercial platforms such as Sysdig Secure, Aqua Security, Wiz, and Prisma Cloud may be suitable for organizations that need broader visibility and security management.
Before choosing a tool, evaluate its features, supported environments, integration options, maintenance requirements, and total cost. Most importantly, combine scanning with secure configuration, controlled access, continuous monitoring, and a clear remediation process.